What to run
Open JWT Decoder. It stays in the browser.
How to read the result
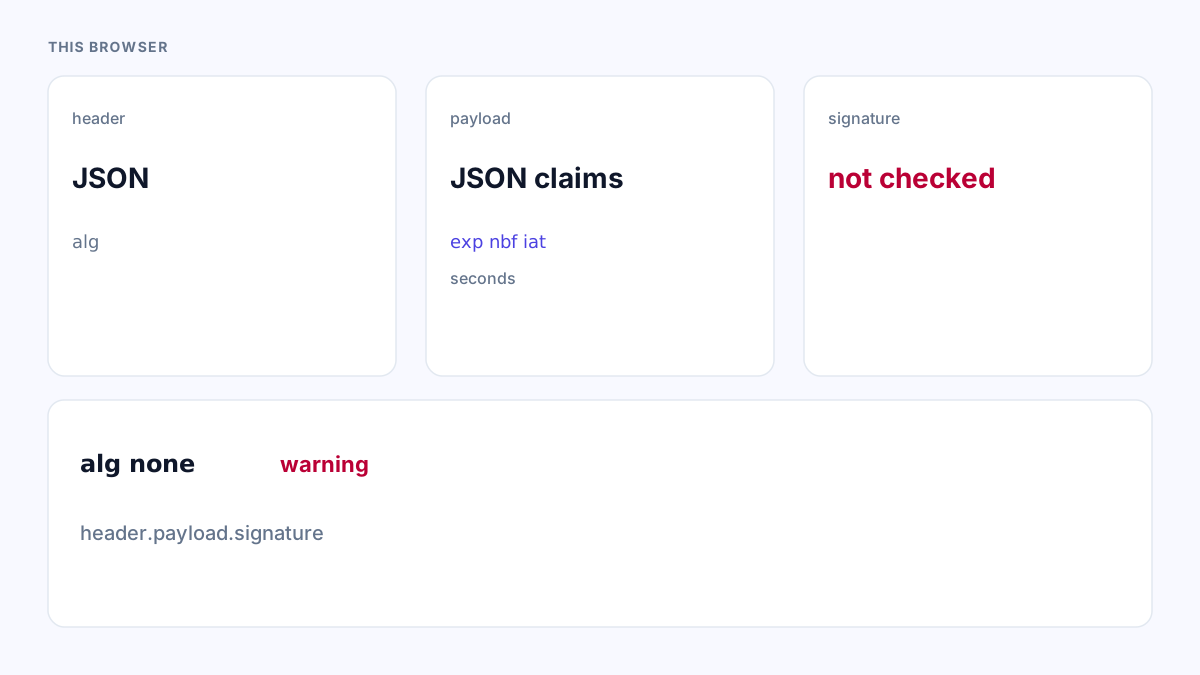
A successful decode means the segments were valid Base64url JSON.
It does not mean alg was honoured or the signature matched.
none in the header is a warning, not a pass.
What to open next
Do not chain into Hash Generator to check the signature. HMAC verification needs the secret, which this tool does not ask for and should not.