What to run
Open HTML Escape. It stays in the browser.
How to read the result
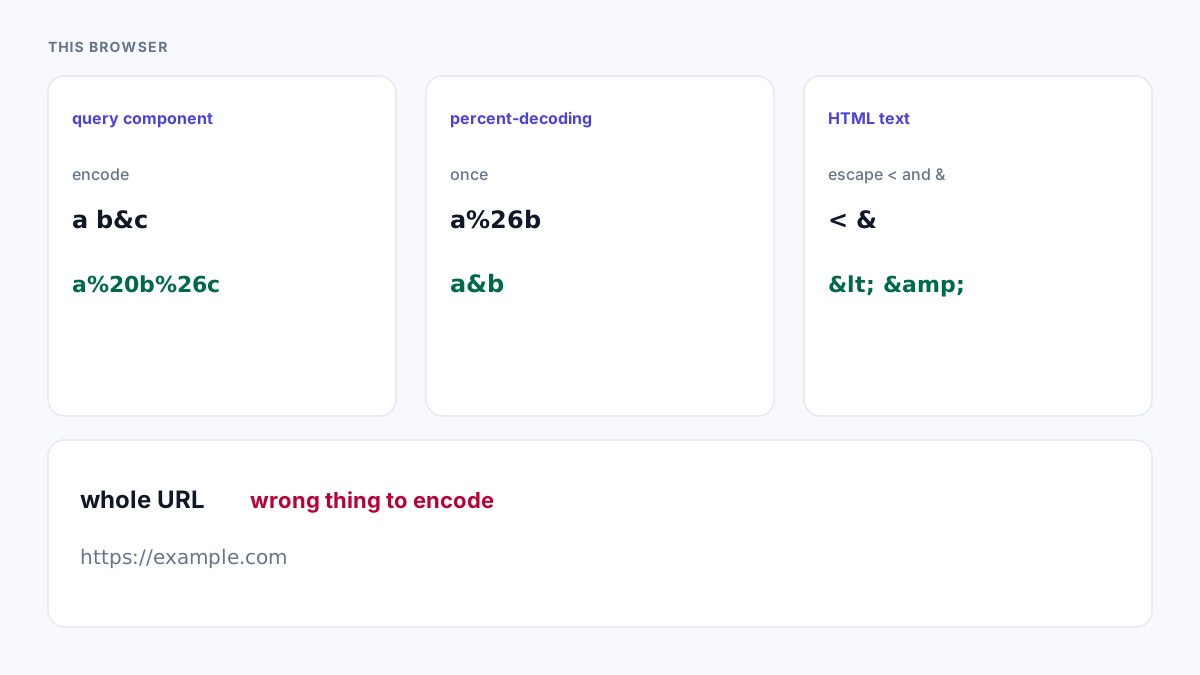
< becomes <. & becomes &.
That is safe to put in element text.
It is not safe inside a URL attribute by itself, and it is not a sanitiser for a whole HTML document.
What to open next
Open URL Encoder for href values. It stays in the browser.
Open Graph Generator already emits escaped tags if you use its snippet. It stays in the browser.